DISCOVER + MONITOR
Discover and monitor autonomous-agent activity alongside employee AI use, so the operating picture includes more than named chat tools.
We use cookies to help you navigate efficiently and perform certain functions. You will find detailed information about all cookies under each consent category below.
The cookies that are categorized as "Necessary" are stored on your browser as they are essential for enabling the basic functionalities of the site....
Necessary cookies are required to enable the basic features of this site, such as providing secure log-in or adjusting your consent preferences. These cookies do not store any personally identifiable data.
Functional cookies help perform certain functionalities like sharing the content of the website on social media platforms, collecting feedback, and other third-party features.
Analytical cookies are used to understand how visitors interact with the website. These cookies help provide information on metrics such as the number of visitors, bounce rate, traffic source, etc.
Performance cookies are used to understand and analyse the key performance indexes of the website which helps in delivering a better user experience for the visitors.
Advertisement cookies are used to provide visitors with customised advertisements based on the pages you visited previously and to analyse the effectiveness of the ad campaigns.
Other uncategorised cookies are those that are being analysed and have not been classified into a category as yet.
AI SECURITY / PEOPLE + AGENTS
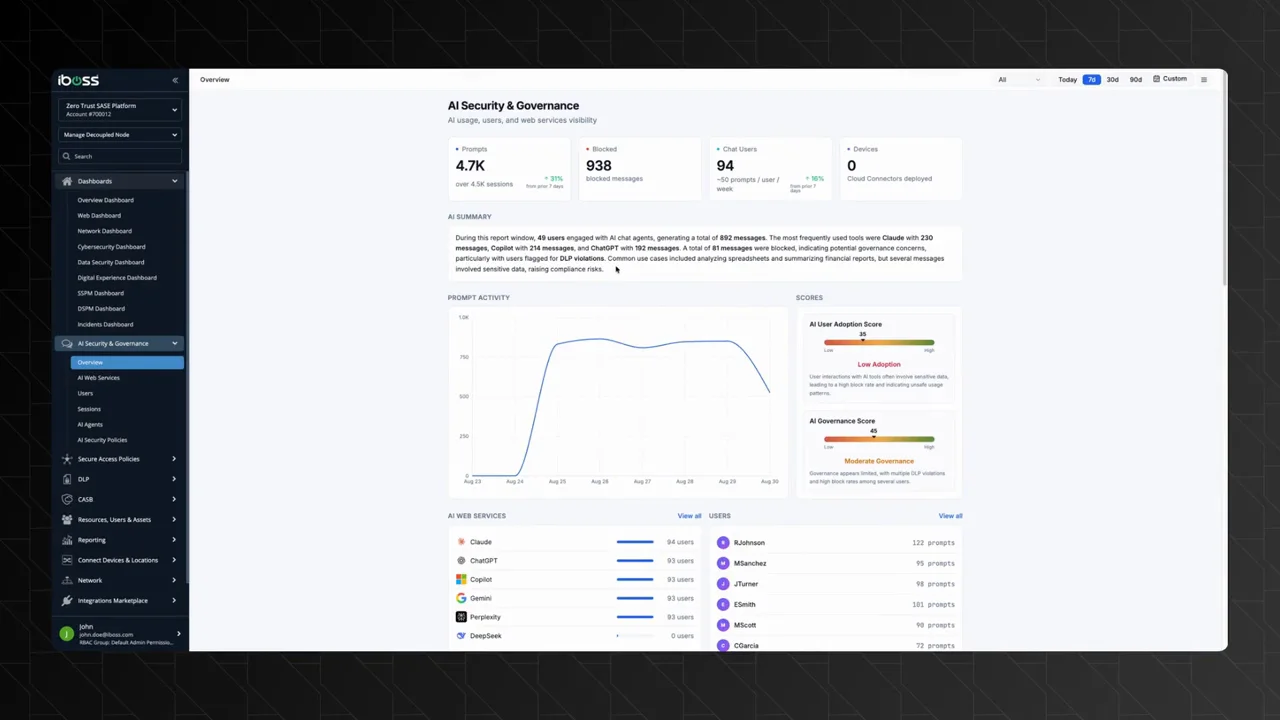
AI adoption does not need a blind spot. iboss gives security teams a single place to see AI activity, prevent sensitive data sharing, and apply policy to the people, tools, and autonomous agents connecting to the web.
WATCH / 04:02
See how iboss provides visibility, data protection, and policy control for enterprise AI use.
01 / THE OPERATING REALITY
Employees are using AI assistants in browsers. Autonomous agents are beginning to reach domains, tools, APIs, and applications. Both create new data paths that security teams need to see and govern without stopping legitimate work.
02 / CONTROL THE CONNECTION
Discover and monitor autonomous-agent activity alongside employee AI use, so the operating picture includes more than named chat tools.
Apply DLP controls to prevent sensitive data sharing with AI services before it leaves the environment.
Govern agent domains and define which AI services, tools, APIs, or applications are available under policy.
Retain AI conversations and agent activity for review, investigation, and audit workflows.
03 / A POLICY DECISION, INLINE
Recognize AI activity, relevant destinations, and the identity or agent context behind a request.
Apply policy by user, group, tool, or risk instead of relying on a blanket AI block.
Allow, constrain, or prevent sensitive sharing and control access to the agent's approved web-facing tools, APIs, or applications.
Keep conversations and activity available for review with the context needed to understand what occurred.
04 / CONNECTED CAPABILITIES
AI security works best when application, data, and access signals arrive at the same policy engine.
Conversation visibility and data protection for approved AI chat use.
RELATED CAPABILITYContent-aware controls for sensitive data in motion.
RELATED CAPABILITYSignatureless application discovery and granular browser controls.
RELATED CAPABILITYKeep inspection, telemetry, and controls aligned to jurisdictional requirements.
05 / FAQ
iboss provides visibility and policy controls for AI use in browsers and within applications that leverage AI, including plugins and AI assistants for applications such as Microsoft Excel and Word. Unlike AI security solutions limited to browser activity, iboss can secure embedded AI interactions across applications, inspect AI conversations, apply DLP policies to sensitive data, and retain activity for review.
iboss can discover and monitor autonomous-agent activity, govern agent domains, retain agent conversations and activity for review, and control an agent's access to tools, APIs, or applications.
Yes. Policies can be applied by user, group, tool, or risk so security teams can permit useful AI workflows while setting boundaries for sensitive data and higher-risk destinations.
Yes. AI security is strengthened by inline inspection and DLP controls that can prevent sensitive data sharing before it reaches an AI service.
THE NEXT CONVERSATION
Bring the use cases. We will map the visibility and policy controls across your environment.
Request a demo