Named a Leader in the 2026 GigaOm Radar for SASEGet the report →
    IT, security, or MSP/MSSP leader? Take a 1-hour demo, keep a pair of AirPods 4Claim yours →
    Capabilities / DLP

    Data Loss Prevention

    iboss DLP inspects every upload, prompt, and transfer in real time, blocks sensitive data before it leaves, and turns every violation into an incident your team can investigate and close.

    PII · PHI · Credit cards · Credentials · Source code · Labeled documents
    upload inspected · api-keys.jsonscanned
    matcher: PII · 1 unique matchdetected
    policy: block · file capturedenforced
    incident #338 · risk score 85opened
    analyst assigned · story readylogged
    Watch

    See iboss DLP in action.

    Policies, content matchers, and incident response in one console.
    Press O for more options
    Video Thumbnail
    01 / The Problem

    If it can't be labeled, it can't leak here.

    Sensitive files move to unapproved apps and personal storage every day, and most teams cannot see it happening. Label-based DLP only makes the gap sharper: labeling every document is impossible, and the moment one slips through unlabeled, it leaks.

    iboss inspects the content itself, in transit. Labeled or unlabeled, PII in a spreadsheet or credentials in a JSON file, it gets detected and blocked at upload, with full visibility into where your data was headed.

    02 / Policies

    A policy in minutes, enforced in real time.

    Scope it to users, groups, or devices. Point it at destinations. Pick the search criteria and the response. Policies apply top-down in real time across every connected user and device.

    +Source and destination scoping with named exceptions
    +Ready-made content analysis rules like Search for PII
    +Responses: block, capture file, log, alert, set severity
    +Changes take effect instantly across the fleet
    edit dlp policy · defaultenabled
    sourceall users and devices
    destinationall destinations
    exceptions1 · legal team review
    search criteriaSearch for PII · severity high
    response 1any rule triggered → capture file
    response 2any rule triggered → log an event
    03 / Detection

    Every matcher a data security team reaches for.

    Built in and ready on day one. No scripting required to start blocking.

    PIIPersonally identifiable information in content
    Credit Card NumbersCard numbers, plus Track 2 stripe data
    Data LabelsLabeled documents, including Purview MIP labels
    Email AddressesEmail addresses within content
    Phone NumbersPhone numbers within content
    Encrypted FilesFiles that cannot be inspected
    File TypesMatch by true file type, not extension
    File Names & SizeName patterns and size thresholds
    Custom KeywordsYour own keyword lists, globally reusable
    Regular ExpressionsCustom patterns when you need them
    Exact Data MatchExact column matching against your records
    Search PatternsBuilt-in patterns for common data formats
    + VALIDATORSMatched values can be required to pass Luhn, Mod97, IBAN, or ABA checks before they count.
    match qualifiers · piiper matcher
    surrounding text must contain "ssn"enabled
    match must not contain "test"enabled
    validator: Luhn check must passrequired
    limit to file types: spreadsheets, documentsscoped
    5 unique matches → severity highthreshold
    04 / Precision

    Tuned for signal. Quiet on noise.

    Match Qualifiers wrap every matcher with context so a hit means something: what surrounds the value, how it starts and ends, which files count, and whether it validates.

    +Context rules around and inside the matched value
    +Luhn, Mod97, IBAN, and ABA validation checks
    +File size, type, and name limits per matcher
    +Unique and total match thresholds with severity on match
    05 / Incidents

    From violation to closed case.

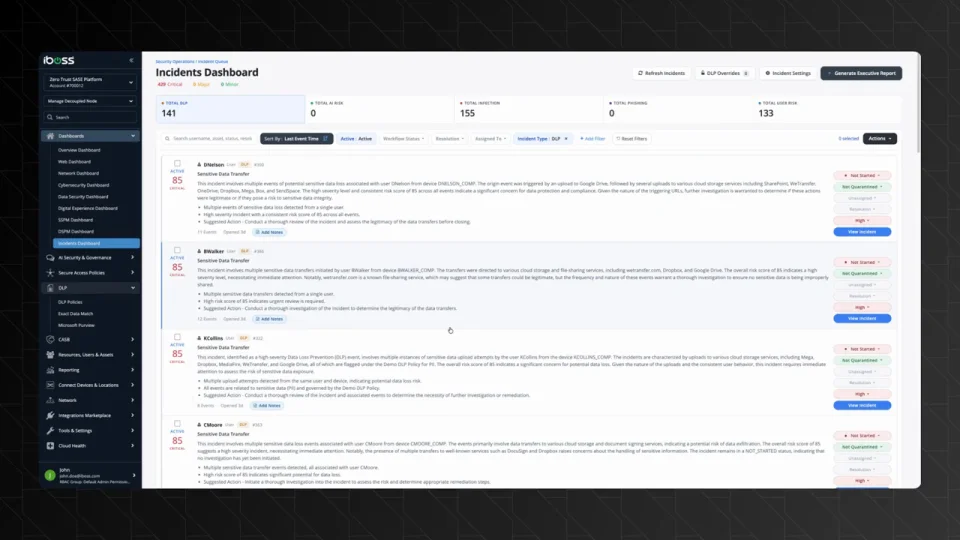
    Events roll up into risk-scored incidents with the full story: what moved, where it went, what was at risk, and the captured file as evidence. Your team works a queue instead of the logs.

    +Risk-scored queue with workflow, severity, and assignment
    +Event timeline with files, domains, IPs, and policy context
    +Captured file evidence and logged samples, downloadable
    +Gap findings that flag log-only rules before data walks
    incident #338 · sensitive data transferrisk 85 · critical
    user: CGarcia · 12 events · opened 3dnot started
    20:07 · api-keys.json → sendspace.com · PIIblocked
    06:54 · employee-records.csv → mega.nz · PIIblocked
    finding: rule only logs this match · switch to block to stop it at submissiongap
    evidencecaptured file · logged samples · event log
    data labels · microsoft purviewsynced
    Highly Confidentialblock transfer
    Confidentialallow + log
    Internalallow
    No label · PII detected in contentblock transfer
    6 data labels syncedauto
    06 / Microsoft Purview

    Purview labels enforced. The label gap plugged.

    iboss reads MIP sensitivity labels in transit and enforces transfer policy the moment a labeled file moves. And when a document was never labeled, content inspection still catches the sensitive data inside it. Labeled or not, it does not leak.

    +Detects Purview MIP labels inside files in transit
    +Block or allow transfers per label, per destination
    +Unlabeled documents get the same protection via content inspection
    +Extends enforcement to web, cloud, SaaS, and AI, no relabeling
    07 / Part of the Platform

    One engine across web, cloud, SaaS, and AI.

    The same DLP engine and policies protect uploads to the web, prompts to AI chat, and files moving into discovered cloud apps: one console, shared incidents.

    +The same matchers govern AI prompts and web uploads
    +CASB discovery feeds destinations automatically
    +Incidents from every channel land in one queue

    Block the leak. Keep the evidence.

    See how iboss DLP blocks sensitive data in real time and hands your team the case file.